
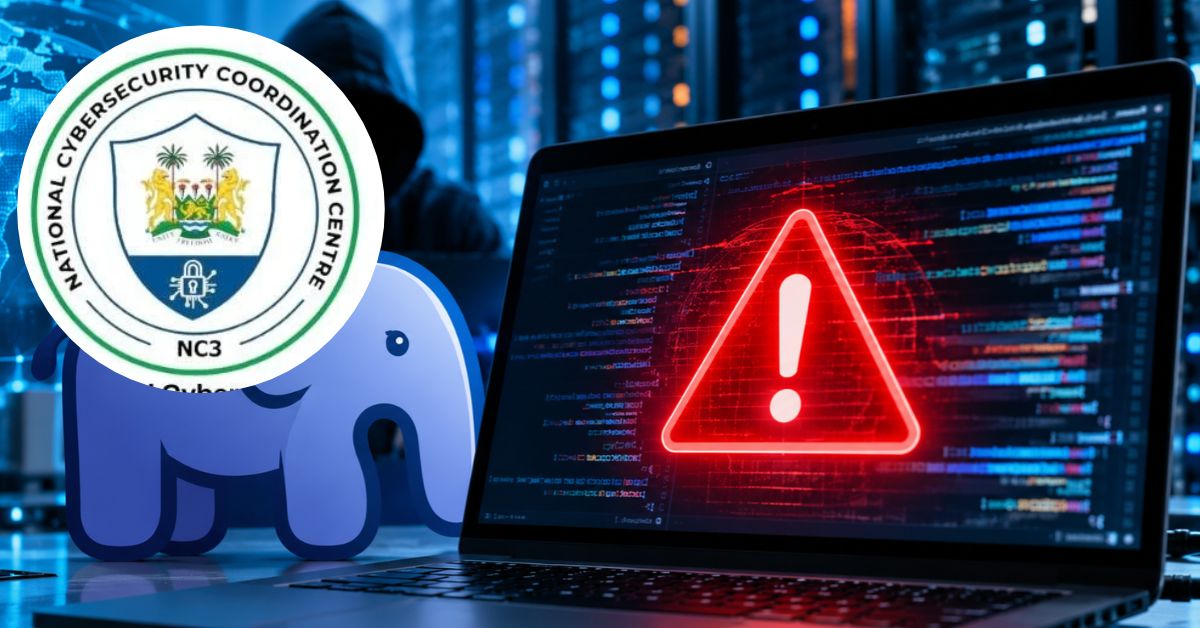
Sierra Leone Cyber Agency (NC3) Warns of Critical PHP Security Flaws Affecting Websites
 Kanja Sesay
The National Cybersecurity Coordination Centre (NC3), through the Sierra Leone Computer Security Incident Response Team (SL-CSIRT), has issued a critical cybersecurity alert, warning government institutions, businesses, website administrators and hosting providers about two potentially dangerous vulnerabilities affecting PHP-based web services.
The warning, reported on Saturday, October 24, 2026, identifies two security flaws, tracked as CVE-2026-109618 and CVE-2026-109619, which have reportedly been assigned a severity score of 9.2 out of 10.
According to the advisory information, the vulnerabilities could allow attackers to execute malicious code remotely on affected web servers without requiring authentication.
The alert has raised concerns about the security of websites and online services as Sierra Leone continues to expand its use of digital platforms across government and private institutions.

PHP is a widely used open-source programming language that supports many websites and web applications worldwide, including systems built using popular content management platforms such as WordPress and Joomla.
The reported vulnerabilities are particularly concerning because of their potential to allow remote code execution, a type of security weakness that can enable an attacker to run unauthorised commands on a vulnerable system.
If successfully exploited, such weaknesses could expose affected organisations to data theft, website compromise, service interruptions and other cybersecurity incidents.
The two vulnerabilities reportedly affect different aspects of PHP’s internal processing.
The first, CVE-2026-109618, is described as a memory corruption vulnerability associated with out-of-memory conditions. According to the reported technical details, specially crafted file-upload requests could potentially trigger the flaw and lead to malicious code execution.
The second, CVE-2026-109619, reportedly involves the reuse of internal application state between requests, creating conditions that could potentially be exploited to interfere with server operations.
The precise exposure of individual websites depends on their PHP versions, configurations and whether the relevant security updates have been applied.
According to the advisory, PHP developers released security updates on October 21, 2026, addressing the reported vulnerabilities.
The versions identified in the alert include PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35.
Organisations operating PHP-based websites and applications have been urged to review their installations and apply the appropriate security updates after confirming the affected versions and official vendor guidance.
Website administrators are also encouraged to review server configurations, monitor suspicious activity and ensure that important data is backed up.
For organisations still using unsupported PHP versions, upgrading to a maintained release is an important step towards reducing exposure to known security threats.
Administrators should also coordinate with their hosting providers to determine whether server-side PHP installations require updates.
The alert reinforces the importance of cybersecurity preparedness as Sierra Leone advances its digital transformation agenda.
Website owners, developers, businesses and government institutions are encouraged to review their cybersecurity arrangements, maintain supported software versions and respond promptly to verified security advisories.
For members of the public, the warning also serves as a reminder of the importance of protecting online accounts, using strong authentication methods and reporting suspicious digital activity.
As reliance on online services continues to grow, timely security updates and coordinated responses to emerging threats remain essential to protecting Sierra Leone’s digital infrastructure.